WiFiT3: free, open-source cross-platform Wi-Fi security audit toolkit
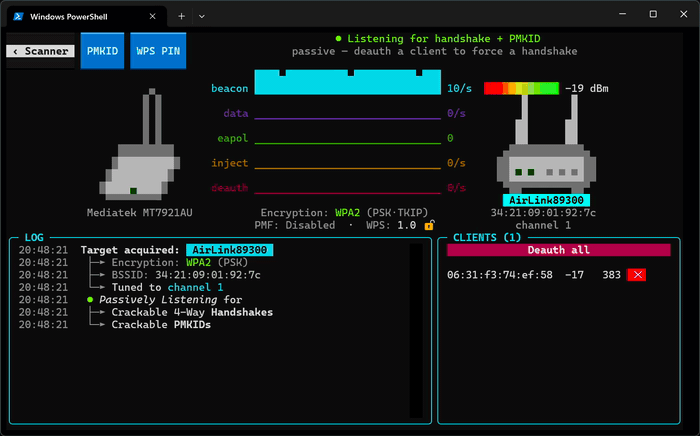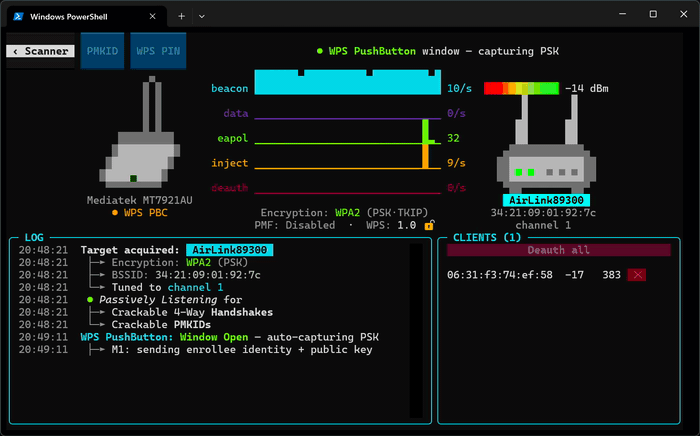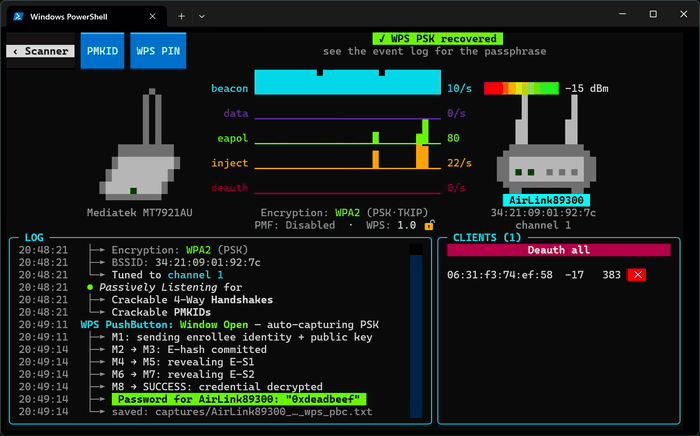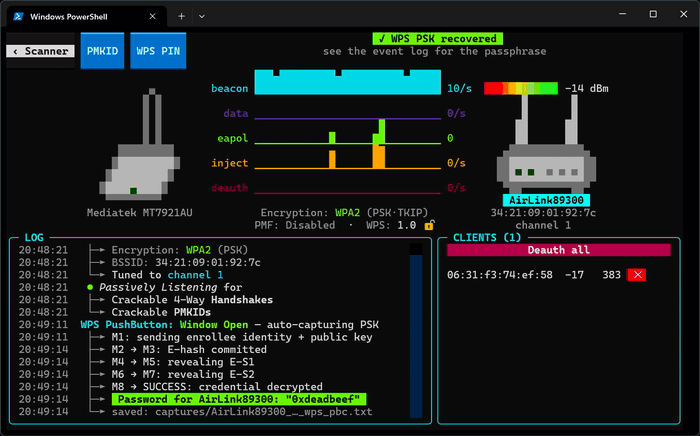
WiFiT3 is a free, open-source Wi-Fi security auditing toolkit that runs across Linux, macOS, and Windows from a single codebase. Instead of wrapping legacy tools, it reimplements the wireless stack in pure Python — using PyUSB to talk directly to supported adapters and Textual for a live terminal UI — so there are no dependencies on aircrack-ng or reaver.
Why it stands out
- Cross-platform with built-in drivers. It ships its own lightweight Python wireless drivers and controls adapters over USB bulk/control transfer, bypassing each OS's native Wi-Fi stack.
- Zero legacy dependencies. Pure Python plus PyUSB and Textual — no external cracking suites required.
- Real-time scanning. Signal strength, encryption type, and device info update live, with multiple adapters able to cooperate on capture.
- Audit artifact retention. Handshake capture and file export are built in, alongside WPS and WEP security testing capabilities.
Supported hardware
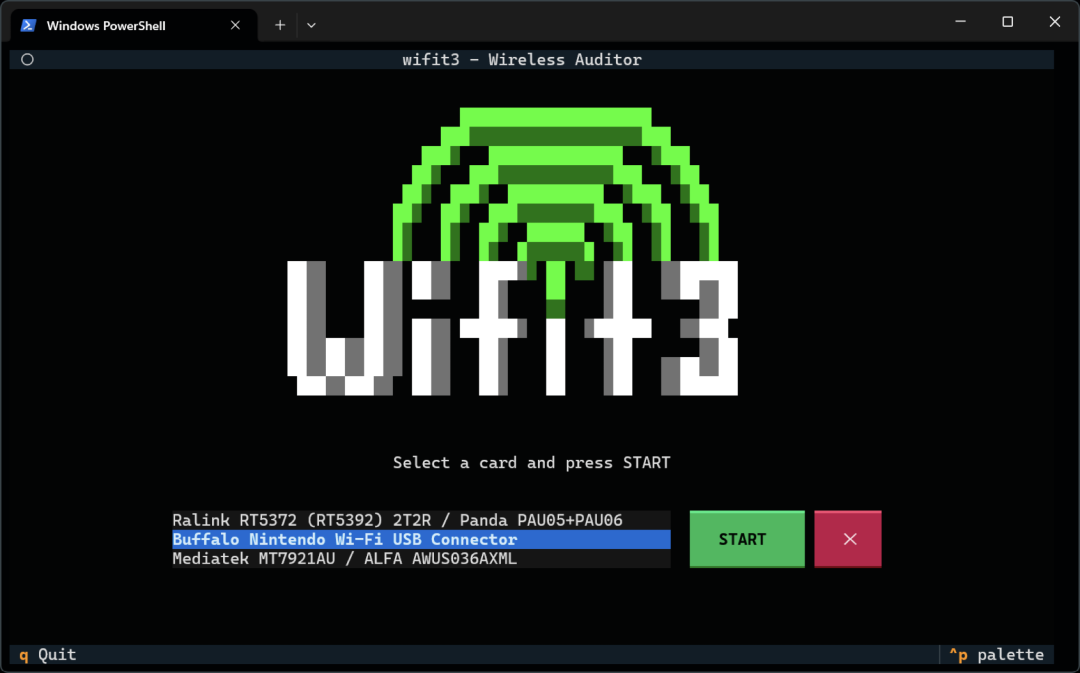
WiFiT3 works with a range of common Wi-Fi chips exposed over USB, including AR9271, MT7612U, MT7921AU, RTL8812AU, RTL8822BU, and RT3070. Multi-adapter setups can split 2.4 GHz / 5 GHz channel hopping or dedicate an adapter to injection.
Reconnaissance and analysis
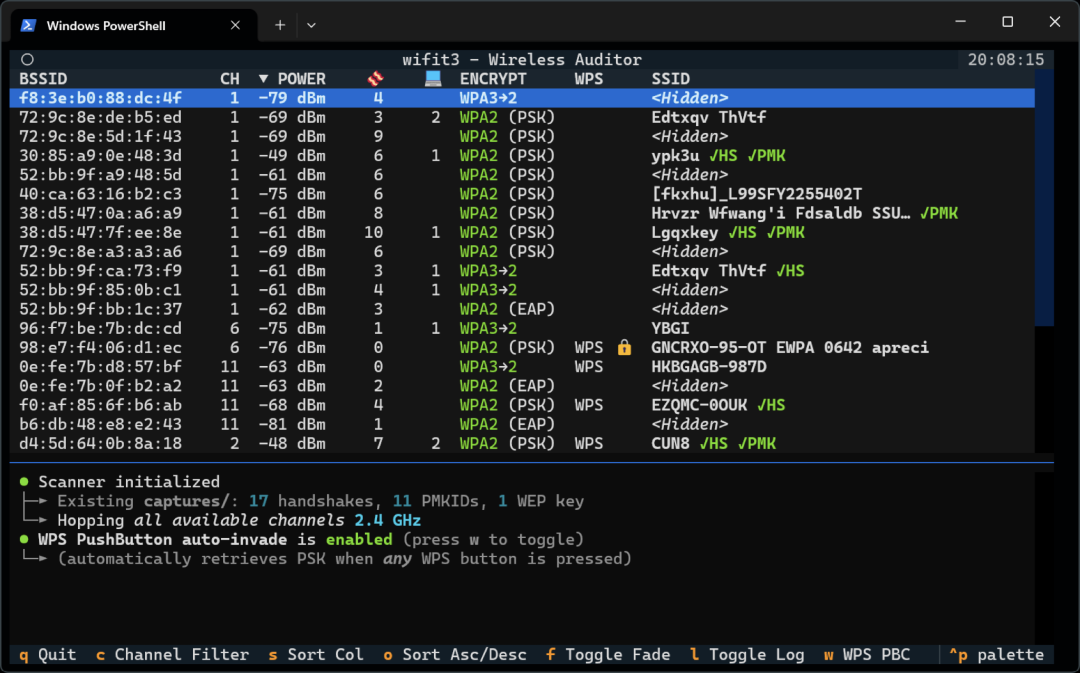
The toolkit aggregates captures across several adapters at once and tracks:
- Multi-adapter aggregation — capture packets across interfaces simultaneously, with a dedicated adapter selectable for injection.
- Live scanner — 2.4 GHz and 5 GHz channel hopping, signal strength, cipher suites, and WPA3/SAE transition mode detection.
- AP and client identification — vendor and class recognition, plus router brand/model pulled from WPS beacons.
- Hidden network de-cloaking (VAP) — correlates a hidden BSSID with known visible peers of the same class.
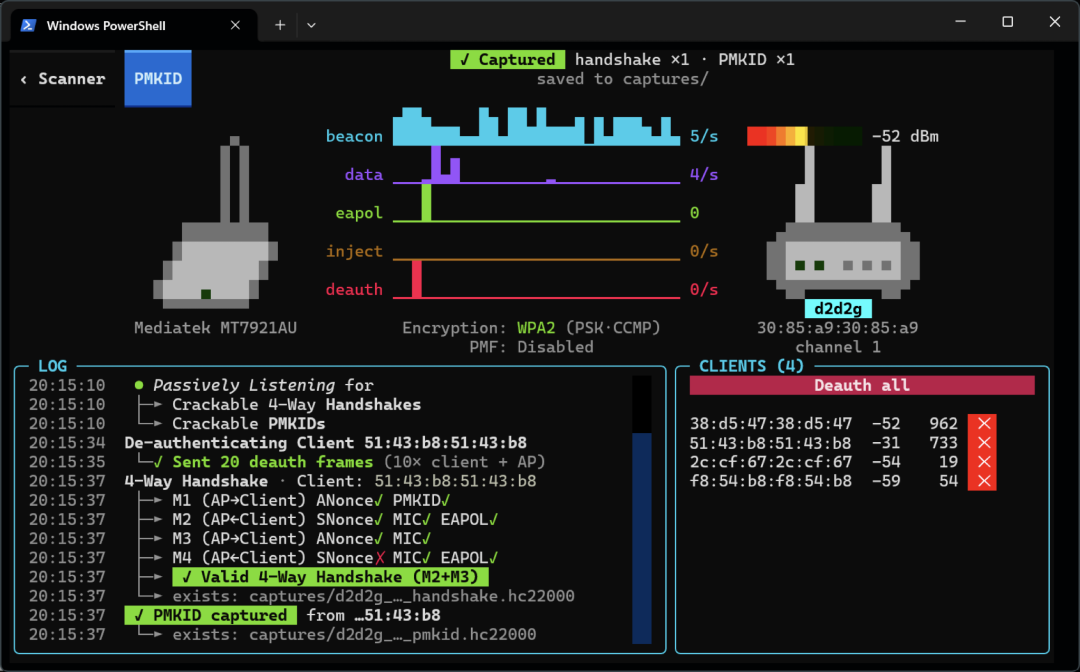
- Packet dashboard — real-time visualization of beacon, data, injection, and deauthentication packet rates.
Capture and auditing
On the capture side, WiFiT3 covers the standard authorized-testing workflow:
- WPA/WPA2 handshake — passive sniffing and directed deauthentication, exportable as
.pcapand.hc22000. - PMKID collection — active association and passive sniffing of PMKID key material (
.hc22000). - EvilTwin WPA3 downgrade — clones an AP and evicts clients via CSA, BTM, and deauthentication to capture the handshake, on single or multi-adapter setups.
- WPS recovery suite — PixieDust (Null/Static Secret PRNG weaknesses), PushButton (extracts the plaintext WPA PSK when the physical button is pressed), and PIN brute force with known-PIN database and lockout monitoring.
- WEP suite — pure-Python ARP replay, ChopChop, fake authentication, and PTW key recovery.
First launch auto-initializes configuration per OS: udev permissions and modprobe rules on Linux, WinUSB via UAC on Windows, and an authorization prompt on macOS — with an uninstall path provided to restore the original drivers.
Responsible use
WiFiT3 is a security auditing instrument intended for authorized testing on networks you own or have explicit permission to assess. Capabilities described here are summarized for awareness; always operate within applicable law and the scope of your engagement.
IOTTourChina covers open-source IoT and connectivity tooling as part of its device and integration resource. Details should be confirmed against the project's official documentation.